

6 Jan 2026


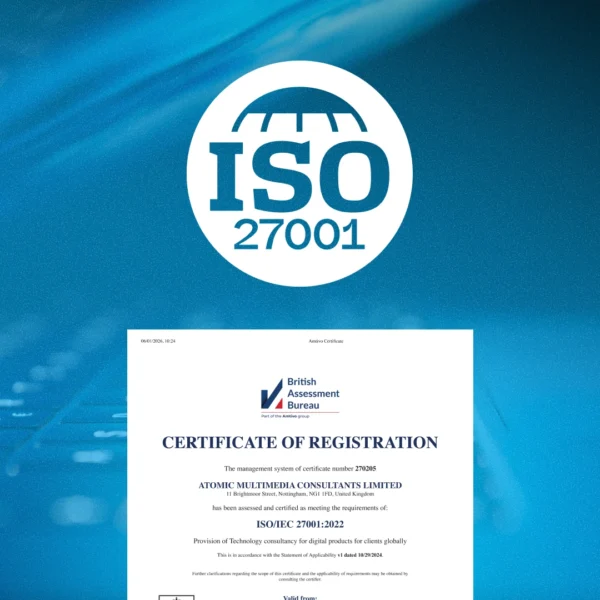
This certification marks a significant milestone for Atomic and reinforces our commitment to protecting sensitive information, managing risk responsibly, and maintaining the highest standards of security for our clients and partners.
ISO/IEC 27001 is widely regarded as the gold standard for information security. Achieving certification demonstrates that Atomic has implemented a robust framework for identifying, managing, and reducing information security risks across the organisation.
For our clients, this means added confidence that their data is handled with care, integrity, and industry-leading best practices. For our team, it reflects a culture of accountability, continuous improvement, and shared responsibility for security.
Reaching this milestone was a collective effort across the business. From defining policies and processes to embedding security into our day-to-day operations, the certification journey required focus, collaboration, and a long-term commitment to doing things the right way.
Achieving ISO/IEC 27001 certification is a testament to the dedication and professionalism of our team. As information security is fundamental to the trust our clients place in us, this certification not only validates our approach today, but also strengthens our foundation for the future.
While achieving ISO/IEC 27001 certification is an important achievement, it’s not the end of the journey. Information security is an ongoing responsibility, and we remain committed to continually reviewing, improving, and strengthening our controls as technology and risks evolve. If you’re looking for a technology partner that takes security seriously from day one, we’d love to talk. Get in touch to learn how we can support your next project and protect what matters most.